Microsoft 365 Password Spraying Attack Hits 78 Accounts
A large-scale password spraying attack has hit Microsoft 365 accounts across dozens of organizations, generating more than 81 million login attempts in just two weeks. Security researchers at Huntress tracked the campaign between June 12 and June 26, and confirmed that attackers successfully compromised 78 accounts spanning 64 organizations. What makes this campaign stand out isn't just its scale. The
ChocoPoC Malware Hides in Fake GitHub Security Exploits
Security researchers have uncovered a malware campaign that turns the tools of the trade against the people who use them. A newly identified threat called ChocoPoC malware is spreading through fake proof-of-concept exploits on GitHub, targeting the very researchers and penetration testers who download these files to study vulnerabilities. The campaign flips a familiar trust relationship on its head, using
Anthropic Begins Restoring Claude Fable 5 Access This Week
Anthropic has begun restoring Claude Fable 5 access. The U.S. Department of Commerce lifted export controls that had blocked the model for months. Anthropic confirmed the news in a statement on X, saying access to Fable 5 would start rolling out on Wednesday. Mythos 5, the company's other high-capability model, stays limited to a small group of approved organizations for
ShinyHunters Disputes NAIC Data Breach Claims After Leak
A major insurance regulator just found itself at odds with the hacking group that broke into its systems. The NAIC data breach, first detected on June 11, has turned into a public dispute over exactly what was stolen and how serious the damage really is. The National Association of Insurance Commissioners, which oversees insurance regulation across all 50 states, confirmed
KDDI Data Breach Exposes Email Logins for 14 Million Customers
One of Japan's largest telecom providers has confirmed a serious security incident. A KDDI data breach has exposed the email credentials of up to 14.22 million customers — not just from KDDI itself, but from five additional internet service providers that shared the same compromised email infrastructure. The breach raises urgent questions about how shared systems across telecoms can turn
New Mistic Backdoor Fuels KongTuke Ransomware Attacks
Security researchers have uncovered a new piece of malware called the Mistic backdoor, and it is built for one purpose: to stay hidden for as long as possible. First spotted in active attacks in April 2026, Mistic has been deployed against organizations in insurance, education, IT, and professional services. Researchers believe it is the latest tool from KongTuke, a criminal
OpenAI Daybreak Cybersecurity Push Targets Patching
Finding security flaws in software has never been easier. Fixing them is a different story. That gap between discovery and remediation has grown into one of the most serious problems in modern cybersecurity, and OpenAI just made it the central focus of its expanded Daybreak cybersecurity initiative. The company rolled out a new wave of tools and partnerships under the
LastPass Confirms Data Breach in Supply Chain Attack
Password manager giant LastPass has confirmed a data breach affecting customer information stored in its Salesforce environment. The incident traces back to a supply chain attack on Klue, a third-party market intelligence platform, which gave hackers access to authentication tokens that connected into LastPass's CRM systems. Importantly, the breach did not touch user vaults or LastPass's core infrastructure. How the
WhatsApp Phishing Attack Spreads Via Fake Docs
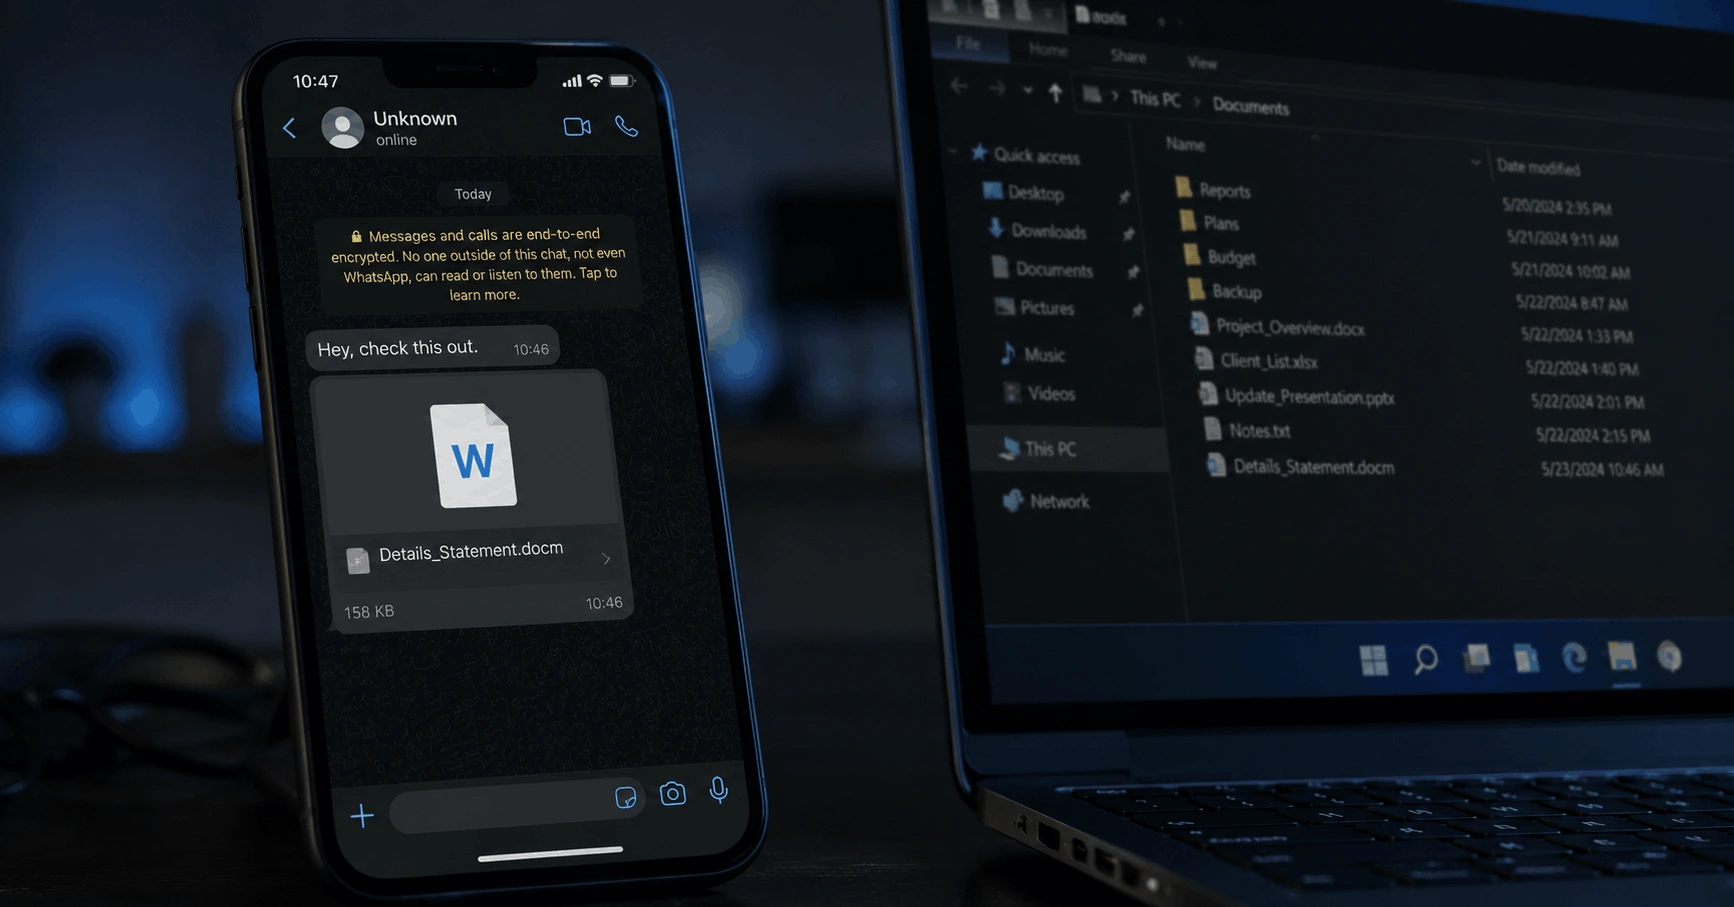
A WhatsApp phishing attack is currently spreading across at least 11 countries, and it is more convincing than most. The messages arrive from people you know. The attachments look like invoices, financial reports, or account notices. And if you open one on a Windows PC, attackers can quietly take full control of your machine. Cybersecurity researchers have identified an active
Prinz Eugen Ransomware Targets Your Newest Files
A new ransomware strain called Prinz Eugen is drawing attention from security researchers, and its approach sets it apart from most threats in this space. Rather than encrypting files in a random or alphabetical order, Prinz Eugen targets the most recently modified files first. The goal is to lock down the data that matters most before defenders have a chance