Coder Cloudflare Breach Delivered Malware to Developers
A trusted software registry spent roughly 14 hours handing out poisoned code, and the developers pulling from it had no reason to suspect a thing. That is the short version of the Coder Cloudflare breach, an attack against a development platform used by Dropbox, Palantir, Square, Mercedes-Benz, and parts of the U.S. government. Attackers never edited a single line in
US Charges Russian Over TVRAT Malware Attack on Freelancers
A phishing operation that ran quietly for a year and a half has finally put its alleged operator in front of a US judge. Federal prosecutors in California have indicted a Russian national over a campaign that planted TVRAT malware on the computers of 80,000 freelancers. The attack never touched a corporate network. Instead, it arrived through a messaging system
Sality Botnet Seized After 23 Years of Crypto Theft
A piece of malware that first appeared in 2003 has finally run out of road. Law enforcement agencies across several countries seized the infrastructure behind the Sality botnet this week, and private security firms handled the technical side of the operation. The malware survived 23 years of antivirus updates, operating system rewrites, and earlier cleanup attempts. Now its command network
Fire Ant Hackers Hijack Cisco Routers to Spy on Networks
Routers rarely get attention. They sit in racks, push traffic, and run untouched for years at a time. That quiet reliability is exactly what Fire Ant hackers learned to exploit, because a compromised router watches everything and raises no alarm. Investigators recently unpicked a Chinese espionage operation that turned Cisco networking gear into long-term surveillance equipment. The group has moved
Claude Session Hijacking: Malware Drains Paid AI Accounts
Anthropic has started emailing Claude users with an unwelcome message. Malware sitting on their own computers stole active login sessions. Attackers then used those sessions to sign in and drain the usage that victims had paid for. This wave of Claude session hijacking did not begin with a flaw in the AI platform, because it began on the victim's own
Carhartt Data Breach Exposes 12.9 Million Accounts
Millions of people who once ordered a jacket or a pair of work pants now have a security problem on their hands. The Carhartt data breach has pushed personal details from more than 12.9 million customer accounts onto a dark web leak site, and the exposed records go well beyond email addresses. Names, phone numbers, and home addresses sit in
Zimbra Server Attacks Hit 274 Systems as Patching Lags
Hundreds of email servers around the world now sit under attacker control. A scan on August 22 found 274 compromised Zimbra instances, and the Zimbra server attacks behind that figure have not slowed down. A patch for the underlying flaw arrived back in July. Yet thousands of systems still run vulnerable code, so the window for exploitation stays wide open.
Operation Jackal IV: 58 Arrests in Global Fraud Takedown
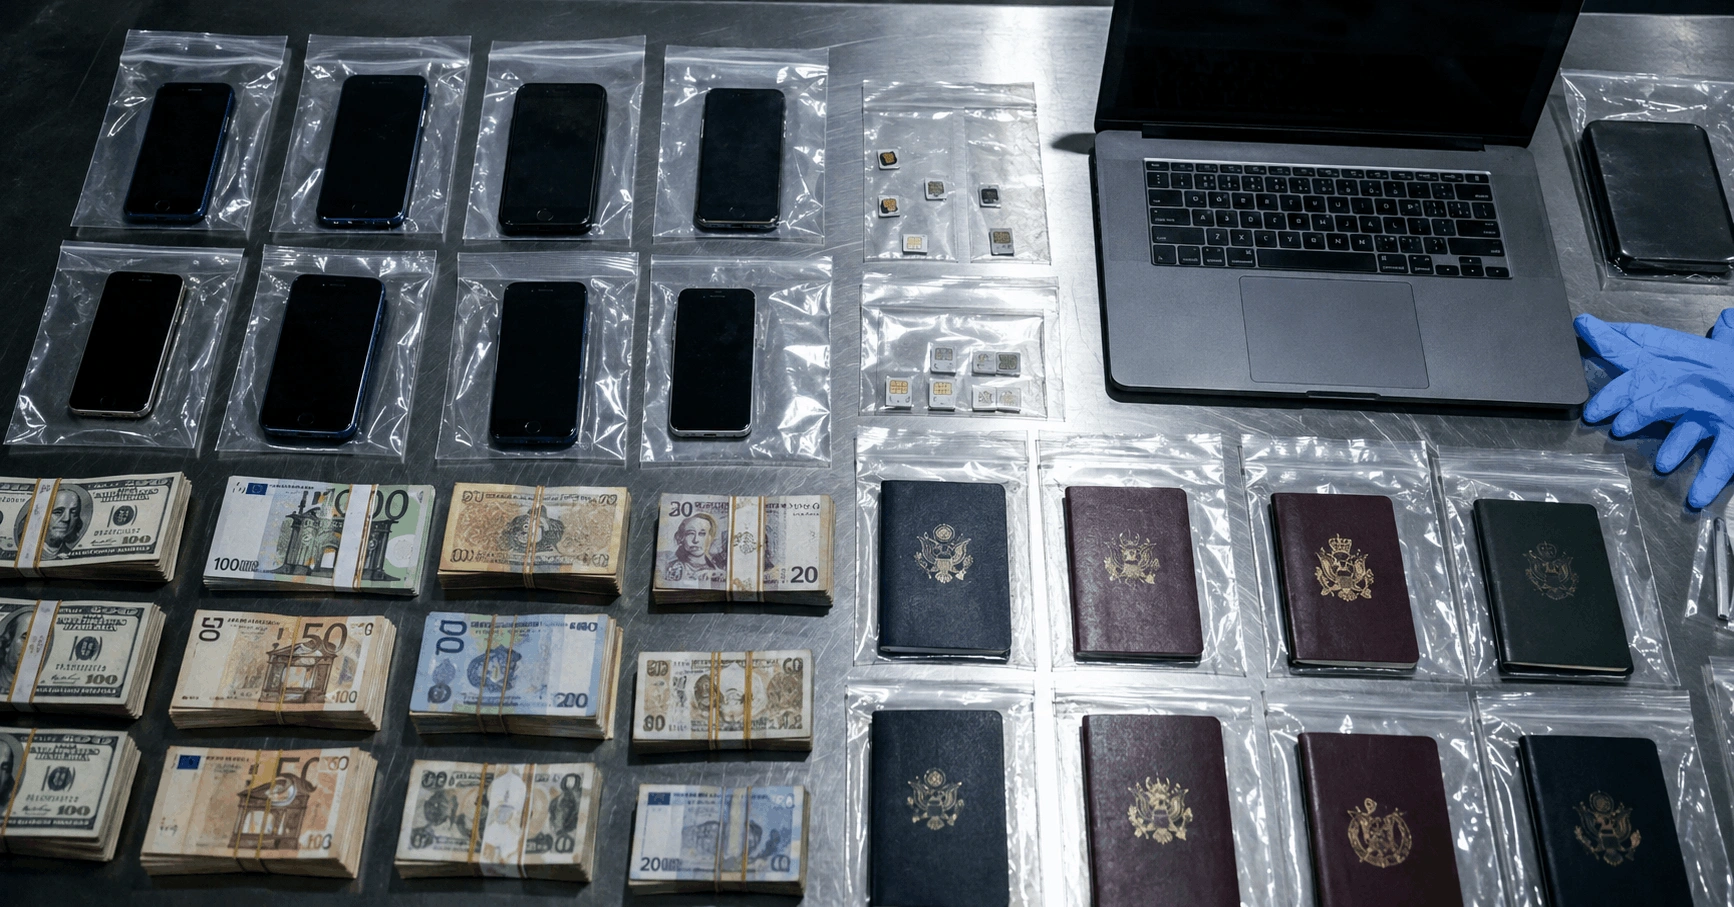
Police forces in 22 countries have closed one of the biggest fraud investigations of the past year. Operation Jackal IV ran from November 2025 through June 2026, and it ended with 58 arrests. Investigators also identified 263 more suspects tied to cybercrime networks run by West African organized crime groups. INTERPOL coordinated the work, and the results open a rare
MoYu Proxy Botnet Hijacks Android Car Head Units
A car's touchscreen looks harmless. It plays music, shows maps, and handles the climate controls. But researchers have now found malware that turns those screens into infrastructure for online crime. They traced the campaign to MoYu, a threat group that runs a proxy botnet built from hijacked consumer devices. This time the target was the Android head unit sitting in
ToxicPanda Android Malware Blocks Google Play Via VPN
A banking trojan aimed at Android phones has returned with a much sharper set of tools. The ToxicPanda Android malware now asks victims to approve a VPN connection, then uses that access to cut the phone off from Google Play. Once that link goes dark, the device loses the checks that would normally catch a threat like this. Security scans,