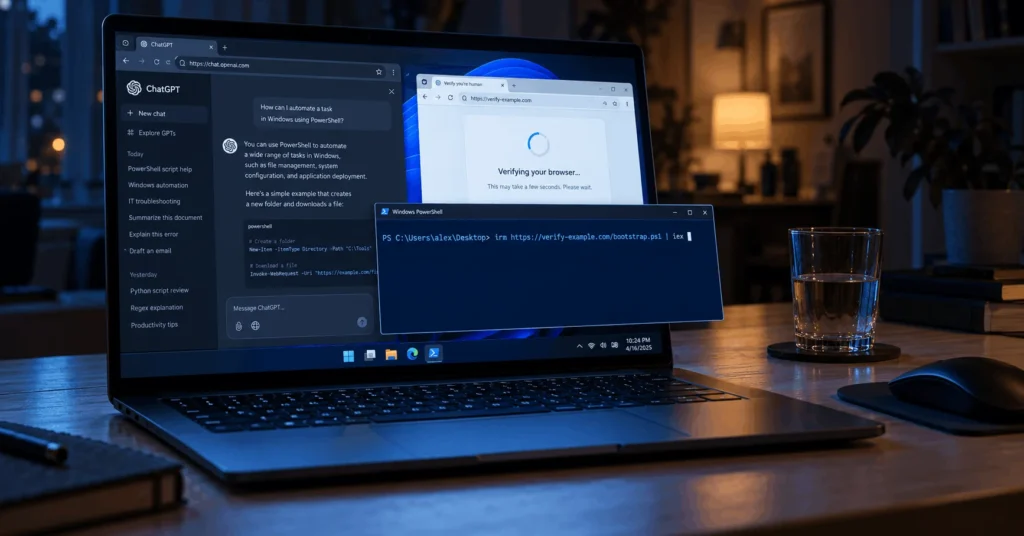
A new malware campaign starts where almost nobody thinks to check: inside a ChatGPT page. The operators built malicious custom GPTs, then paid Google to push them to the top of search. Victims trusted what they saw and followed the steps. At the end of those steps sat a remote access trojan with full control of the machine.
How malicious custom GPTs abuse a trusted domain
OpenAI lets anyone build a tailored version of ChatGPT from instructions, extra knowledge and a few skills. Creators can then publish those builds for other people to install. They sit on chatgpt.com like any other part of the service, and that arrangement is the whole draw for an attacker.
Malicious custom GPTs borrow the trust people already place in OpenAI, and nobody squints at a chatgpt.com link. So the lure lands with far more force than a random phishing page would. OpenAI retires the feature on December 11, but this campaign is live right now.
One build went by the name Plus 5.6 and sent users to a so-called backup site on Google Sites. Two familiar brands in a row do a lot of quiet work, since neither domain sets off any alarms. The victim never sees a suspicious URL until it no longer matters.
The fake Cloudflare check that starts the attack
That backup page showed a fake Cloudflare check, the sort most people click past without a second thought. This one asked for something odd, though. It wanted visitors to copy a PowerShell command and run it locally to prove they were human.
That trick has a name, and it is ClickFix. It hands the hard part of the attack to the victim, so the operator never needs an exploit. Malicious custom GPTs never touch the malware themselves, because they only supply the directions that lead to it.
Run the command and it quietly installs a malicious MSI package. The installer drops a real, signed app next to a modified DLL. When the signed app starts, it loads that tampered file. Most security tools trust signed software, so the loader walks straight past the checks that would flag an unknown file.
What the trojan does on an infected PC
The payload gives its operator a wide view of the machine. Audio capture, camera feeds, remote desktop sessions, file searches and extra payloads all sit on the same menu. Work email, banking logins and client files end up within easy reach of anyone who ran that command from one of these malicious custom GPTs.
Persistence disguised as printer software
The malware plants two footholds: a Run key in the Windows Registry and a scheduled task. Both carry the name Canon Configuration Reader, which reads as harmless printer software. Delete one and the pair come back, and that stubborn return makes a useful warning sign.
A campaign that keeps changing
Researchers traced at least 40 incidents back to the Google Sites page, though only two clearly began inside a malicious custom GPT. OpenAI pulled the first build offline by September 25. A second appeared two days later, tied to the same operation, and it still ran when the research went public.
Early waves used a Canon-signed host application, and later ones moved to a Stardock-signed one. How they hide and deliver the loader changed too. Yet the payload stayed identical, which points to one group polishing its tooling.
An encrypted archive built from scratch
One stage of the chain stands out for sheer effort. Rather than dump everything into a single encrypted blob, the attackers built a custom archive with its own folder tree, a sort of homemade encrypted zip file. It opens with a small header, then an index of 1,128 entries that each record a parent, a size and a key of their own.
Why malicious custom GPTs are hard to block
Most of the chain runs in memory or leans on files that look normal on disk, so signature scanning has very little to grab. Defenders do better by watching what processes actually do. PowerShell calling msiexec.exe to launch an MSI from a temp folder is one clear flag, and a signed app starting from an odd path under %LOCALAPPDATA%\Programs\ is another.
Blocklists offer little help either, because malicious custom GPTs sit on a domain nobody wants to block. The instructions arrive through a service the user chose to open, so reputation filters see nothing worth flagging. That gap between the host and the payload is the entire point.
How to stay safe
One simple habit blocks this entire class of attack, and it costs nothing. Never run a terminal command that a web page tells you to run. No real verification check will ever ask for that, Cloudflare included. Close the tab.
Malicious custom GPTs will keep surfacing until the feature retires in December, and copycats will find the next trusted platform soon after. Sponsored results deserve the same doubt, because paid placement buys visibility and nothing else. A VPN helps too, since it encrypts your traffic and hides your browsing from network snooping. It will not stop you pasting a command, though, so treat tools and habits as a pair.
Final Thoughts
The appeal of malicious custom GPTs is easy to see. Google Ads brings the traffic, chatgpt.com brings the credibility, and the victim supplies the click. Every part of that chain works exactly as designed.
AI platforms will keep letting users publish content to one another, so this pattern will outlive the custom GPT feature. Malicious custom GPTs are only the current wrapper on a very old trick. Treat advice from any AI tool the way you treat advice from a stranger, because the model does not vouch for whoever set it up.
